AWS Route 53 DNS in WHMCS: Customer Zones, Templates and Record Management
Connect Route 53 with WHMCS customer DNS self-service, type-aware record editing, reusable templates and supported automatic hosted-zone workflows.
A hosting business can use Amazon Route 53 for DNS without wanting every customer to become an AWS administrator. The customer usually needs a simpler task: point a website, update mail routing or publish a verification record for a service they are connecting.
PD AWS Route 53 DNS brings supported hosted-zone and record management into WHMCS, with customer DNS self-service and staff tooling. The host keeps the AWS provider connection, while customers work with zones assigned to their account through the client portal.
The module also supports reusable record templates, package limits, zone snapshots and optional automatic zone creation. That makes it useful as part of a hosting offer, rather than merely another place for staff to view a list of DNS records.
Keep AWS access with the hosting team
The host connects its Route 53 account through the module’s provider configuration. Staff can then browse the relevant hosted zones and open their records from WHMCS.
Customers do not need the host’s AWS management credentials to perform their permitted DNS tasks. They use the assigned-zone interface in the billing portal, where the account relationship is already established.
That separation is valuable when the AWS account contains several customers’ zones or other resources. Customer DNS access should be a specific service capability, not an invitation to share a provider-wide administrative identity.
The Route 53 connection guide explains the practical setup. The connection and its intended permissions should fit the operations the host plans to provide; a successful preliminary check does not independently test every possible future write.
Understand the hosted zone and delegation
A Route 53 public hosted zone contains the records used to route a domain and its subdomains. AWS explains that model in its public hosted-zone guide.
Creating the zone and making it authoritative for the domain are related but separate tasks. The intended domain delegation needs to point to the nameservers assigned to that zone. An unused zone in an AWS account does not make the public internet query it automatically.
For a host introducing a DNS service, that means the initial workflow should identify the correct account, zone and delegation. The module’s zone management makes the records accessible, while the registration and nameserver arrangement still needs to match the service being offered.
Use the hosted-zone guide for that setup. This article concerns the supported public DNS workflow, not administration of every private VPC zone or every Route 53 feature.
Put routine DNS tasks in the customer portal
Once a zone is linked to the intended client, the customer can view and manage its supported records from WHMCS. The module provides a DNS navigation route and relevant domain or service links, with placement and wording settings for the host.
That helps a customer who already knows how to sign in to manage their hosting. They can find the appropriate DNS service without requesting another provider-console account or asking staff to copy every TXT value on their behalf.
The ownership step matters. Staff should review the assigned account and provider-zone identity before treating a visible backend zone as ready for customer access. The client-access guide covers the module’s controls.
Imagine a customer connecting a new application to a subdomain. They obtain the application’s required target, open their assigned zone, add the supported record and complete the application’s own verification. The module handles the DNS write; the external application decides whether it can observe the intended result.
That is a hypothetical workflow showing the product’s purpose, not a named customer result or a promise of instant global propagation.
Use an editor designed for each record type
PD AWS Route 53 DNS uses a type-aware record editor. An address record, MX record and SRV record require different fields, so the interface adapts to the selected type rather than treating every operation as an unexplained text entry.
The staff view includes search, type selection and sorting, plus supported import and export controls. That makes it easier to locate a particular record when the zone contains more than a small starter set.
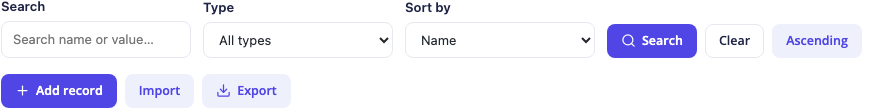
*Actual administration crop. The zone’s demonstration hostname and the outer version area are excluded. These are supported record controls, not a demonstration of an AWS console or advanced resource-alias picker.*
For customer work, the record grid shows the relevant type, name, value and TTL with editing actions. A website change, a mail target and a verification token can therefore be approached as distinct tasks.
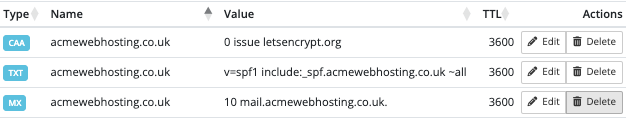
*Actual customer record-table crop with demonstration domain values. No provider credential or live customer information appears. The sample mail and authentication entries are not records to copy into another domain.*
Supported validation helps with format errors. It does not establish that a destination is the one the customer’s application requires, and the module should not be sold as exposing every advanced AWS resource alias configuration. Follow the record-specific task guides for the supported workflow.
Make website, mail and verification records easier to manage
The ordinary customer requests are often the most useful marketing examples. A company moving its website may need an address change. Another may retain the website but move email. A third may need a TXT record to verify control with an application.
PD AWS Route 53 DNS gives those customers a place to manage the supported values in their own zone. They can inspect existing records and change the intended entries without requiring provider-wide access.
The correct records still come from the actual service arrangement. A mail-provider change may involve MX and authentication entries, while an application verification value can be unique to the customer. Do not replace the whole zone with a generic example to solve one request.
The MX guide and TXT verification guide show those tasks. They turn a broad “DNS management” claim into something a buyer can recognise: the routine changes their customers actually need to make.
Standardise new zones with record templates
A hosting team often repeats the same base record structure for a particular offer. Templates let staff define a reusable record set and apply it to appropriate zones rather than rebuilding the structure manually each time.
That can support a more consistent product handoff. A host could prepare the intended website and mail-record baseline for one service, then review the zone-specific values before using it for a new customer.
A template does not know every customer’s external mail or application setup. It should represent a known offer, with the target records reviewed before application, rather than be advertised as universally safe for every existing zone.
The Route 53 template guide provides the procedure. Reuse is useful because it expresses a deliberate configuration more consistently, not because it removes the need to understand the domain.
Connect zone creation with new customer services
The module’s optional automatic-zone workflow can create an appropriate hosted zone in response to supported domain and service events. That connects DNS setup with the commercial process already happening in WHMCS.
For example, a host selling a defined hosting product can plan zone creation and an appropriate starter template as part of that service. The result is a clearer onboarding path than relying on a separate reminder after each order.
Automatic zone creation and registrar nameserver changes should remain separate choices. Any takeover behaviour depends on the supported platform and registrar operation and should be enabled deliberately, rather than changing an existing customer’s delegation unexpectedly.
Use the automatic-zone guide to review the actual events and settings. Confirm the resulting zone and delegation for the intended service instead of assuming a completed billing event proves public DNS is ready.
Define DNS as part of the hosting package
Package controls can limit the number of zones associated with relevant product groups. That gives the hosting business a way to express the DNS service it sells rather than treating customer access as an unbounded shared facility.
A provider might include DNS management with its hosting offer and use a different allowance for another service. The practical setup should reflect the actual customer relationship and the module’s supported entitlement rules.
That is useful for both staff and buyers. Staff know which product arrangement provides the capability, and the customer can understand what is included without needing to interpret an AWS account inventory.
Keep snapshots and maintenance in the staff workflow
PD AWS Route 53 DNS includes BIND-format zone snapshots with scheduled and attended controls. They can help preserve record information before changes and support the module’s reviewed restore workflow.
Snapshots are DNS information, not website files or mailbox data. Restore behaviour also depends on the released importer and its safety-snapshot path, so do not promise an exact replacement or automatic recovery of every deleted zone.
Maintenance and tracking observations help staff review provider presence and relationships. They are not a substitute for public DNS checks, an application’s verification or proof that an apparently orphaned zone is safe to delete.
Those distinctions keep the offer coherent: the customer gets supported record self-service, while the hosting team keeps the broader provider, backup and lifecycle decisions.
Explore PD AWS Route 53 DNS for WHMCS
Explore PD AWS Route 53 DNS for WHMCS if Route 53 is part of your DNS infrastructure and you want it connected to your customer portal and hosting workflows.
Start with the intended public zone, delegation and client assignment. Add the supported record tasks, templates and automation that match the service you sell. The result is a focused Route 53 management experience in WHMCS, with the hosting business’s offer at the centre.
Frequently asked questions
Can customers manage Route 53 records inside WHMCS?
Yes. PD AWS Route 53 DNS provides supported record management for zones assigned to the customer’s account, with host-controlled navigation and access configuration.
Do customers need an AWS account or the host’s management key?
They use the module’s client-area interface for the assigned zone. The host retains the configured AWS provider connection rather than distributing its administrative credentials.
Does creating a hosted zone change the domain’s nameservers automatically?
Creating a zone and delegating the domain are separate tasks. Any supported automatic nameserver change is a deliberate configuration choice, not an inherent result of zone creation.
Can it help with MX and TXT verification records?
Yes. Use the supported type-aware editor and the exact values required by the customer’s mail or application provider. The external service still performs its own verification.
Can I reuse a standard record set?
Yes. Templates support repeatable configurations for appropriate zones. Review the target and actual service values before applying one to a live domain.
Does the module expose every Route 53 capability?
No. Evaluate the documented module workflow rather than assuming full AWS console parity, private VPC management or advanced resource-alias features.
Are zone snapshots the same as a website backup?
No. They preserve DNS record information. Website, mailbox and registration recovery are separate tasks, and the module’s released restore limitations still apply.
